
Short answer: a strong password is long, random and used for only one account. Length and randomness matter far more than swapping letters for symbols. Because nobody can remember dozens of long random passwords, the practical answer is a password manager that creates and stores them for you, plus multi-factor authentication (MFA) on your important accounts, so a stolen password alone isn’t enough.
This guide explains why, separates what security standards require from websites from what’s good advice for you, and finishes with a checklist you can work through today.
What makes a password strong
Attackers rarely guess passwords one at a time by hand. They use software that tries enormous numbers of likely candidates: common passwords, dictionary words, names, dates, keyboard patterns, and passwords leaked from other websites. A password is strong when it isn’t on any of those lists and can’t be predicted from a pattern.
That leads to three properties:
- Length: more characters means more possibilities to try.
- Randomness: each character or word is chosen unpredictably, not from your life or a familiar pattern.
- Uniqueness: the password isn’t reused anywhere, so a leak from one site can’t unlock another.
The US Cybersecurity and Infrastructure Security Agency (CISA) sums up the same idea in three tips in its guide to strong passwords: make them long (at least 16 characters), make them random, and make them unique.
Why length matters
Every extra character multiplies the number of possible passwords. If each character is picked at random from a set of 94 printable characters, each one adds about 6.6 bits of randomness, which is the base-2 logarithm of 94. Ten more random characters therefore add roughly 66 bits, which multiplies the number of possibilities by about 2⁶⁶.
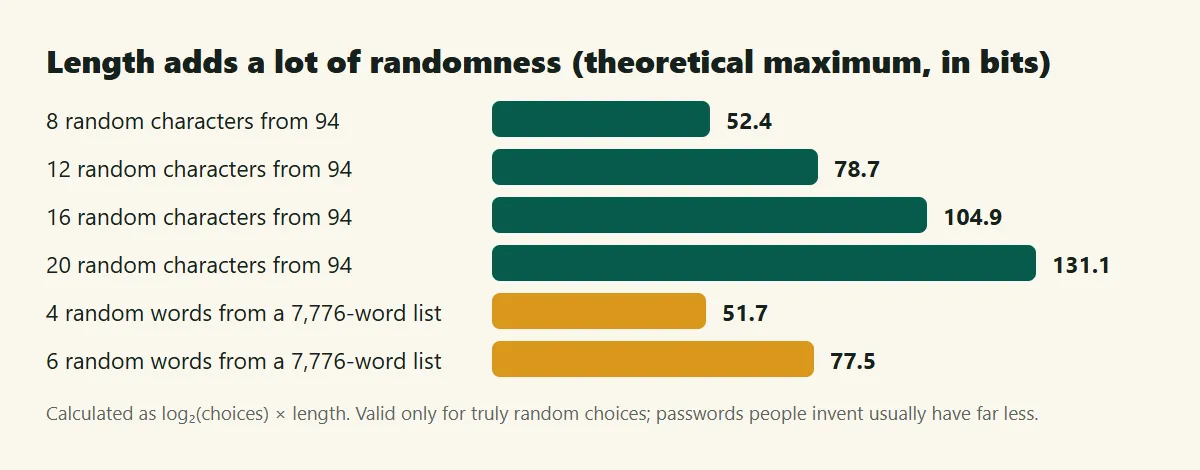
These are theoretical maximums, calculated as log₂(choices) × length. They only apply when every choice is truly random.
The chart shows why the industry has moved towards longer passwords. In the latest US digital identity guidelines, NIST SP 800-63B-4 requires services that rely on a password alone to accept nothing shorter than 15 characters, and those using it as part of MFA to accept nothing shorter than 8. NIST also says services should allow passwords of at least 64 characters, so long passwords and passphrases aren’t cut off.
Randomness vs predictable patterns
A long password isn’t automatically strong. Password2026Password2026 is 24 characters, but it’s built from a common word, a year and repetition: exactly the patterns guessing tools try first. Likewise, the classic tricks of capitalising the first letter, adding 1! at the end, or swapping a for @ are well known to attackers and add very little.
Real randomness comes from a process that doesn’t involve your preferences: a password generator, or picking words with dice or software. The theoretical numbers in the chart above only hold for that kind of choice. A password a person invents usually has far less randomness than its length suggests.
Strong passwords vs passphrases
There are two good styles, and both can be strong:
- A random string, such as 20 characters of mixed letters, numbers and symbols. It packs a lot of randomness into a short length, but it’s hard to remember. That’s fine when a password manager remembers it for you.
- A passphrase: several random, unrelated words. CISA suggests 5 to 7 unrelated words, and the UK National Cyber Security Centre recommends combining three random words. Passphrases are easier to type and remember, which makes them ideal for the few passwords you must memorise, such as your password manager’s master password or your computer login.
The key word in both is random. A favourite song lyric or a famous quote is a phrase, but it’s predictable, and attackers use word lists that include such phrases.
The ARAIJA Password Generator creates random-string passwords from 8 to 64 characters, with 20 as the default, using your browser’s secure random generator (Web Crypto). It runs only in your browser, and nothing is sent or saved. It doesn’t create word-based passphrases.
Unique passwords for every account
Reuse is one of the most damaging habits, because breaches are common. When a website is breached, attackers try the leaked email and password combinations on other popular services. This is called credential stuffing. If you reused that password, every account that shares it is at risk, no matter how strong it looked.
Using a different password everywhere turns a breach at one site into a contained problem: change that one password and you’re done.
Password managers
A password manager stores your passwords in an encrypted vault, generates new random ones, and fills them in for you. You only need to remember one strong master password.
The evidence for them is strong enough that NIST requires services to allow password managers and autofill, and says they should permit pasting passwords. NIST notes that password managers have been shown to increase the likelihood that people choose stronger passwords. CISA also recommends using one.
Password managers bring two extra benefits that are easy to miss:
- They help against phishing. A manager normally offers to fill a password only on the website address where it was saved, so a look-alike fake site often gets nothing.
- They make uniqueness effortless. You never need to invent or remember a new password again.
Choose a reputable manager, protect it with a strong passphrase, and turn on MFA for the manager itself.
Multi-factor authentication
Multi-factor authentication (MFA) adds another factor to password-based sign-in, such as an authenticator app or a security key. When MFA is enabled and enforced, a stolen password alone is not enough to sign in. Passkeys are a different option: where a service supports them, a passkey can replace password-based sign-in and offer phishing-resistant authentication. A passkey is not necessarily a second factor added on top of a password.
Turn it on first for the accounts that would hurt most to lose: your email (which can reset everything else), your password manager, banking, and your main social and work accounts.
Not every method is equally strong. NIST treats one-time codes sent over the telephone network (SMS or voice calls) as a restricted option, and tells services to consider warning signs such as a SIM change or number porting before relying on them. The OWASP Multifactor Authentication Cheat Sheet compares the common methods and describes attacks such as SIM swapping and phone-number takeover. For password-based MFA, prefer an authenticator app or a security key over SMS when possible. If a service supports passkeys, consider switching to passkey sign-in instead of using a password. SMS-based MFA is generally better than using only a password, but it is more vulnerable to phone-number attacks.
Phishing and credential theft
Even a perfect password can be handed over by mistake. Phishing messages imitate trusted organisations to trick you into entering your password on a fake site or revealing a code. The US Federal Trade Commission’s guide on recognising and avoiding phishing scams describes typical stories scammers tell: they’ve noticed suspicious activity or log-in attempts, there’s a problem with your account or payment information, or you need to confirm personal or financial details by clicking a link.
Protective habits:
- Go to important sites by typing the address or using a bookmark, not from a link in a message.
- Be suspicious of urgency, threats and requests for codes.
- Never share an MFA code with anyone who contacts you.
- Let your password manager’s autofill act as a check: if it doesn’t recognise the site, stop and look closely.
Weak password examples (synthetic)
These examples are invented for illustration. They show patterns that guessing tools try early:
| Example | Why it’s weak |
|---|---|
123456789 |
A sequence that sits near the top of common-password lists |
qwerty123 |
A keyboard pattern plus a number |
Bangkok2026! |
A place, a year and a symbol at the end: all predictable |
P@ssw0rd |
Character swaps that attackers’ tools apply automatically |
Somsak1990 |
A name and birth year, often findable online |
iloveyouiloveyou |
Common phrase, repeated |
NIST requires services to check new passwords against a blocklist of commonly used, expected or compromised passwords, so many of these should be rejected when you try to set them.
What standards require from websites, and what’s advice for you
It helps to keep these separate, because NIST’s rules are written for the services that check passwords, which NIST calls verifiers.
NIST SP 800-63B-4 requires verifiers to:
- require at least 15 characters for passwords used alone, or at least 8 when the password is part of MFA;
- check new passwords against a blocklist of commonly used, expected or compromised passwords;
- not impose other composition rules, such as requiring a mix of character types;
- not require people to change passwords periodically, but force a change when there is evidence of compromise;
- not offer password hints or security questions such as “What was the name of your first pet?”;
- allow password managers and autofill.
NIST also says verifiers should allow at least 64 characters and accept all printable ASCII characters, spaces and Unicode.
Practical advice for you comes from that same logic, along with consumer guidance from CISA and the NCSC: use long random passwords or passphrases, never reuse them, store them in a password manager, turn on MFA, and change a password when you have a reason to, such as a breach notification or after typing it into a suspicious site. Changing it on a fixed schedule without a reason isn’t required, and tends to produce predictable variations.
The OWASP Authentication Cheat Sheet, written for developers, summarises the same length guidance and recommends MFA.
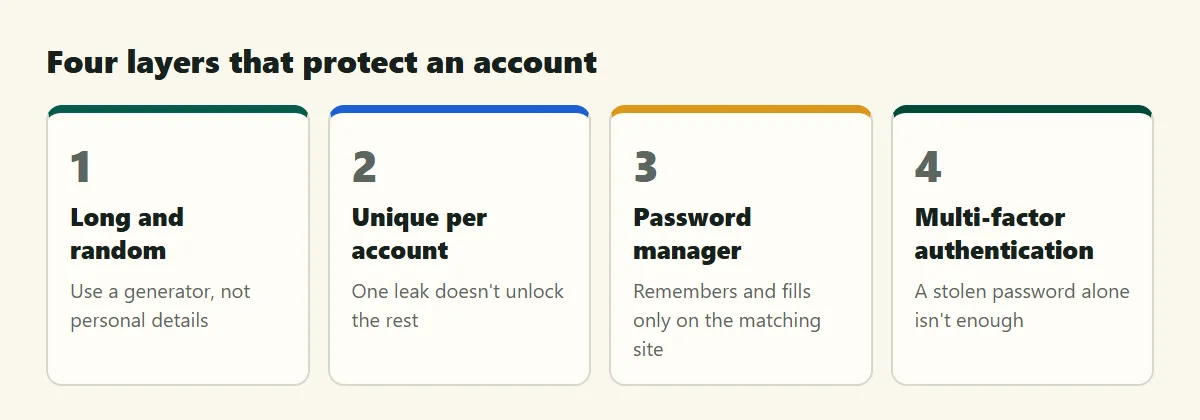
Each layer covers a different way accounts are lost.
Practical security checklist
- Install a reputable password manager and create a long, random passphrase for it.
- Turn on MFA for your email, password manager and bank first.
- Change any password you know you’ve reused, starting with your most important accounts.
- Let the manager or a generator create every new password.
- Remove password hints and weak recovery details where you can.
- Keep your phone, computer and browser updated.
- Treat unexpected login links and code requests as suspicious.
- When a service reports a breach, change that password, and any place you reused it.
Common misconceptions
- “Symbols are always required.” NIST tells verifiers not to impose composition rules. A long random password without symbols can be very strong. Some sites still demand symbols, so follow their rules when you must.
- “Changing passwords every 90 days keeps me safe.” NIST says verifiers shouldn’t require periodic changes; change when there’s evidence of compromise.
- “A complex-looking password is a strong password.” Patterns like
P@ssw0rdlook complex but are predictable. - “My account isn’t interesting to hackers.” Guessing and credential stuffing are run by software against huge lists of accounts, not chosen one by one, and a reused password is valuable precisely because it unlocks other accounts.
- “A password generator makes me safe on its own.” It solves guessability, not phishing, malware or reuse.
FAQ
How long should my password be?
For passwords a manager stores, around 20 random characters is a comfortable choice; ARAIJA uses 20 as its default. For passphrases you memorise, use several random words. If a site has its own limits, follow them.
Is a passphrase safer than a random string?
Neither is automatically safer: it depends on how much real randomness each has. Passphrases are easier to remember; random strings are compact. Both are strong when chosen randomly and long enough.
Should I write passwords down?
A password manager is better. If you must write one down, keep it physically secure and never with the account name.
Is it safe to use an online password generator?
Choose one that generates in your browser with a secure random source and doesn’t send or store results. ARAIJA’s generator works this way, but it can’t protect a password after you copy it, so paste it straight into your password manager.
Summary and next step
Make every password long, random and unique; let a password manager remember them; turn on MFA for the accounts that matter most; and watch for phishing. These habits address the ways accounts are actually lost far more than clever character substitutions.
Start with the account that would hurt most to lose, usually your email, and give it a new random password and MFA today.
Sources
- NIST: SP 800-63B-4, Digital Identity Guidelines: Authentication and Authenticator Management
- OWASP: Authentication Cheat Sheet
- CISA: Use Strong Passwords
- OWASP: Multifactor Authentication Cheat Sheet
- UK National Cyber Security Centre: Three random words
- US Federal Trade Commission: How to Recognize and Avoid Phishing Scams